Home
Recommended
Other Links

On September 25, 2026, Mandiant released a report regarding continued mass exploitation of CVE-2026-35273 by the ShinyHunters group. TrendAI’s Zero Day Initiative first reported this CVE to Oracle on June 10, 2026, following an investigation I conducted with Minh Giang and Lucas Miller of TrendAI

I tested eight popular SVG sanitizers and bypassed six of them. In this post, I'll show you how a response header can run JavaScript in Firefox even when the response body is completely harmless XML.

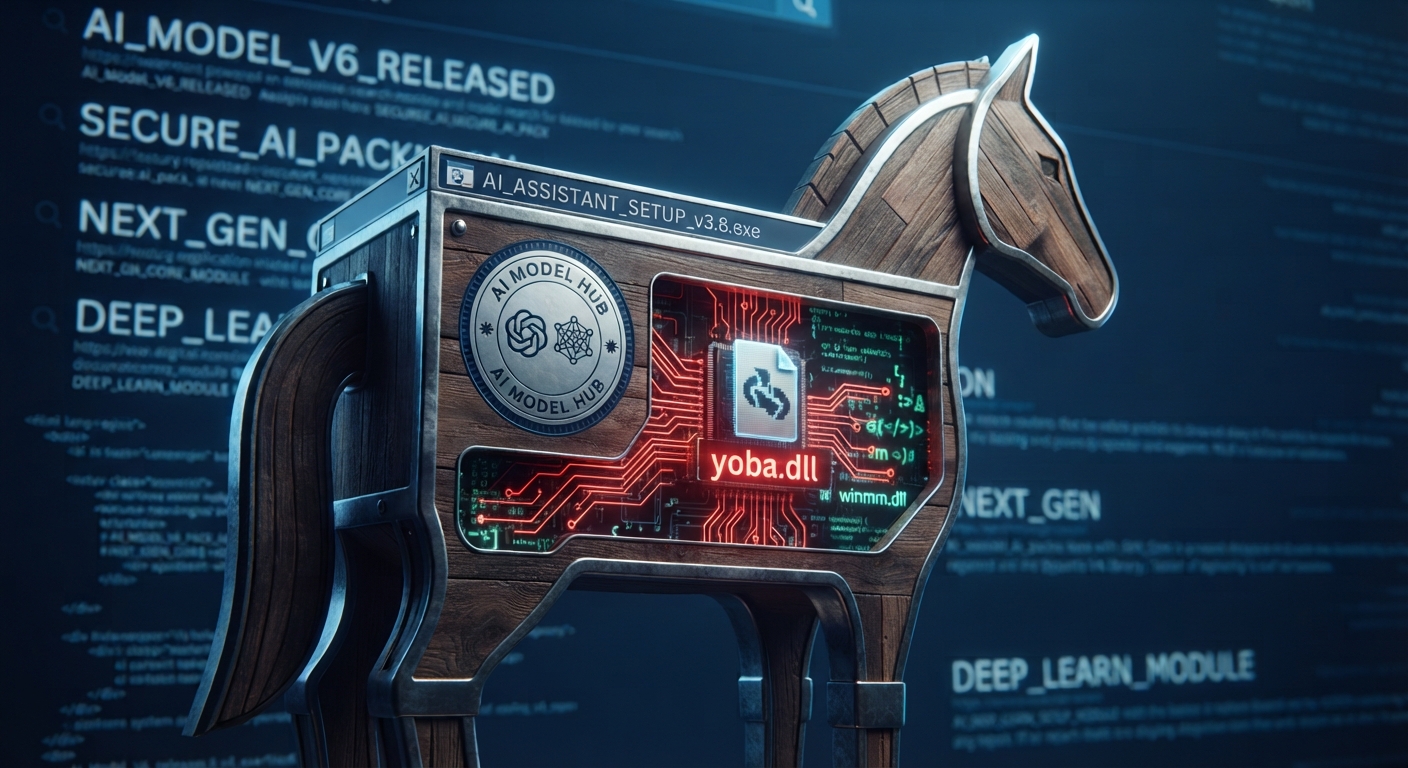
Key Points Check Point Research discovered a campaign we track as Yoba where attackers abuse the popularity of AI tools such as ChatGPT and Claude, creating fake GitHub projects that pretend to be desktop applications like GPT-5.6 Sol, GPT-6 Astra, and Claude Opus. The malware is placed next to legitimate, signed executables from OpenAI and Anthropic so it can be loaded indirectly, a technique commonly known as DLL sideloading, which is often used to bypass security protections. This campaign demonstrates strong operational security (OPSEC) by avoiding dedicated command-and-control (C2) infrastructure and instead relying on Telegram, Tor, Catbox, and DNS over…

**ElectroNG is now free and open source!** Today we are releasing both the desktop application and its core analysis engine under the Apache License 2.0, opening up years of Doyensec’s work on Electron application security to the community.
### Why we are open-sourcing ElectroNG
We launched...
oops i did it again - sabrina-unlock-v2
Key Points Aokigahara, a newly observed infostealer, has been spotted in the wild. An earlier version may have been known as Kamidere or Stygian. The malware includes traditional data theft capabilities targeting browsers, VPN clients, cryptocurrency wallets, FTP/SFTP clients, password managers, and email applications, among other targets. AI applications and development tools are notable targets. The stealer collects authentication files, session data, and configuration files associated with Claude, ChatGPT Desktop, Codex, Cursor, Windsurf, GitHub Copilot, Gemini CLI, and other tools. Stolen AI credentials could offer opportunities for monetization. Usable credentials or session tokens could enable unauthorized access to paid AI…

Key Findings Antidetect browsers obscure the digital identity of their users, enabling a single operator to silently manage thousands of isolated accounts across multiple platforms (including Facebook, TikTok, Instagram, and YouTube), while evading detection systems that look for scams and coordinated inauthentic behavior. Threat actors abuse these platforms, taking over accounts and using them for financial fraud, phishing and malware distribution. These accounts can also be used to coordinate influence operations, which becomes an even greater concern ahead of elections. Social platforms primarily detect coordinated activity at the account and behavioral layer. Antidetect browsers run below the surface enabling them…
TALOS-2026-2439
CVE-2026-10139
A stack-based buffer overflow vulnerability exists in the Mcli functionality of X2000R (version(s): TOTOLINK-X2000R-Gh-V1.0.0-B20250421.1327). A specially crafted HTTP request can lead to arbitrary code execution. An attacker can make an authenticated HTTP request...
TALOS-2026-2440
CVE-2026-10141
A Unsigned Firmware vulnerability exists in the boa Firmware Update functionality of X2000R (version(s): TOTOLINK-X2000R-Gh-V1.0.0-B20250421.1327). A specially crafted firmware binary can lead to arbitrary firmware update. An attacker can make an authenticated HTTP...
TALOS-2026-2438
CVE-2026-10138
A OS command injection vulnerability exists in the boa formUpload() functionality of X2000R (version(s): TOTOLINK-X2000R-Gh-V1.0.0-B20250421.1327). A specially crafted HTTP request can lead to arbitrary code execution. An attacker can make an authenticated HTTP...

Over the past month we collected and analysed 64 Android samples (first seen 2026-09-15 to 2026-10-16) that are all the same thing: a thin dropper that installs a packed second-stage WebSocket RAT. The operators run a web control panel that brands itself with a hawk logo and one of two Chinese names, 黑鹰安卓远控 (“Black Hawk Android Remote Control”) and 雄鹰安卓远程 (“Eagle Android Remote”), over an identical login page and tagline (安全、高效的设备管理控制平台).


Microsoft Browser Vulnerability Research
Oct 16 2026 @ 7:00 AM
Microsoft Edge Extensions Security Team
Browser extension stores review submissions to identify harmful or deceptive behavior before they reach users. Microsoft Edge Extension Security investigated a family of store-hosted extensions that behaved differently depending on how users reached their listings. This design made policy-violating behavior difficult to observe during direct-install review.
Most Android RATs try hard to hide their server. This one barely hides anything and that turns out to be the interesting part. The dropper leaves the key under the mat: a vault-config.json sitting in assets/ right next to the ciphertext it unlocks, holding the key and IV in cleartext.
"A . is all you need!\nToday Microsoft shipped the patch for a vulnerability in Visual Studio Copilot that I reported in August. Microsoft classified it as …"

TL;DR; Our security assessment of LiteLLM (v1.77.7), a widely used open-source LLM gateway, uncovered multiple high-impact vulnerabilities (tracked as CVE-2026-35029, CVE-2026-59823) which have been resolved as of LiteLLM version 1.83.9. The most significant issues stemmed from a missing authorization check on the /config/update endpoint, which allowed any authenticated user (including low-privileged accounts) to modify the proxy's runtime configuration. This single flaw enabled arbitrary file read, administrative account takeover, and remote code execution via malicious Python modules loaded from cloud storage. A separate SSRF vulnerability in the "Clientside LLM Credentials" feature allowed attackers to redirect API calls and exfiltrate provider keys.…

Security audit of Power Grid Model, a C++/Python library for steady-state distribution power system analysis. Sponsored by LF Energy, facilitated by Open Source Technology Improvement Fund (OSTIF) and performed by Shielder.
# Playing It SFAPE: Code Execution in Isolated User Mode
13 Oct 2026 - Posted by Adrian Denkiewicz
It is tempting to think of Windows in terms of a simple model: user mode and kernel mode. If a bug lets a user-mode process gain control of the kernel, it’s game over.
Well, for a long time it...

Before we begin, yes - it's confusing. There are more vulnerabilities with watchTowr IDs in this blog post than there are CVE IDs (assigned by PaperCut), due to PaperCut bundling vulnerabilities and then patch bypasses for those same vulnerabilities into singular CVE IDs.
Paper! It still exists.
We have to admit it - so much is happening right now (F1, GTA6, breakfast) that we barely have time to lovingly tease our most favoritest vendors.
On Thursday, 27 August 2026, PaperCut published an ad

An Iranian Android banking and crypto stealer unpacks from a native RC4 packer, targets 81 financial apps through a phishing WebView, intercepts SMS one-time passcodes and resolves its command server from an encrypted pointer in its own manifest that points to a seller’s bio on a legitimate marketplace. This build’s dead drop was still live, so the real C2 (theapi.the-x-services[.]xyz) is recovered end to end.
Sample (SHA-256) be165239e4fe899b1f2eedf6459d363bca4fe6856fda87a63ba5d4e5e612e1c9
Package ir.novinarya
Loader net.swiftnova.bridge
Live C2 theapi.the-x-services[.]xyz
Published 2026-10-08
Key findings
Two-layer app, native-packed. The installed APK (package ir.novinarya) ships a thin loader shell (net.swiftnova.bridge, 18 KB dex). The stealer itself is a separate Basic4Android payload sealed inside assets/app_cache.db and unpacked on-device by a 29 KB native loader (libuibridge_9203.so) with RC4 (32-byte key, 768-byte drop) then zlib. Asset name, loader name, RC4 key and key transform are re-randomized per build; the unpacked payload is byte-identical across builds.
81 financial targets. It enumerates installed apps (QUERY_ALL_PACKAGES) and matches a hardcoded list of 54 crypto exchanges/wallets and 27 Iranian banking apps.
Phishing WebView, not overlays. Credential theft is a WebView loading an operator-controlled page (WebViewURL) with a JavaScript form-grabber over a native “B4A” bridge. The app requests no accessibility and no overlay permission.
SMS and notification interception. A broadcast receiver and an encrypted 25-bank regex config (X_BANKS) lift account numbers, balances and OTP codes from bank SMS and notifications.
C2 is never a string. The server resolves from an encrypted manifest meta-data value (X_ROUTES, AES-CBC keyed by X_CID) to a URL on basalam.com; the malware reads that profile’s bio and decrypts it to the live, rotating C2.
Dead drop on a legitimate marketplace. The operator rotates servers by editing one bio field. The resolver also carries an unused [GITHUB] branch.
Live C2 recovered. This build’s dead drop, Basalam profile m6AJm5, was live at analysis time. Its bio decrypts to the active command server hxxp://theapi.the-x-services[.]xyz/.
Shared infrastructure, per-build repacking. Five related samples decrypt to two dead-drop accounts: four point at dxoeG7 (now banned) and this one rotated to m6AJm5. The inner stealer dex is identical across all of them, so only the packer and dead-drop config change per build.
Technical analysis
01 The native packer and the unpacking chain
You will find the payload by reading the bootstrap, not by eyeballing the file tree. The APK’s Application class loads a native library and hands it control before any app code runs:
Cisco Talos’ Vulnerability Discovery & Research team recently disclosed vulnerabilities in Adobe, Apple, Foxit Reader, and Microsoft.
The vulnerabilities mentioned in this blog post have been patched by their respective vendors, in adherence to Cisco’s third-party vulnerability disclosure policy.
For Snort coverage that can detect the exploitation of these vulnerabilities, download the latest rule sets from Snort.org, and our latest Vulnerability Advisories are always posted on Talos Intellig

Microsoft Edge Security and Microsoft Threat Intelligence recently disrupted several sustained attack campaigns against Chromium-based browsers. This activity reveals a disturbing trend in which threat actors exploit recently fixed vulnerabilities to target users running versions of Edge and Chrome that have not yet received the fixes. Microsoft thanks our partners at Proofpoint and Volexity for their contributions to this work.
Google CTF. Contribute to google/google-ctf development by creating an account on GitHub.
TALOS-2026-2415
CVE-2026-42532
A path traversal vulnerability exists in the EmailSheet extract\_parts functionality of VisiData (version(s): dev (commit 38b21f78)). A specially crafted .eml file can lead to arbitrary file write. An attacker can provide a malicious file to trigger this...
TALOS-2026-2414
CVE-2026-41958
A path traversal vulnerability exists in the unzip\_http RemoteZipFile extract functionality of VisiData (version(s): dev (commit 38b21f78)). A specially crafted .zip file can lead to arbitrary file write. An attacker can provide a crafted URL to trigger this...
Have you ever felt like a model isn't actually trying to do what you asked? Did you just ask it wrong, or is there something else at play here? In this post, I'll briefly explore this phenomenon, the
Welcome back to yet another episode of "security was taken seriously".
Being who we are (and constantly being exposed to what we see…), we recognize we have been doomed to eternal damnation as we keep on watching security best practices crumble behind “secure by design” public statements. And in the times we live in, where anyone with a prompt window in front of them can say "reproduce the vulnerability, make no mistakes", so are you.
In Greek mythology, Atlas was punished by the gods for misb
Authors: tiszka@chromium.org, bookholt@chromium.org, mattdr@chromium.org
In this document we outline how WebGPU works through the mind of an attacker, our vulnerability research methodologies, and our thought processes in some of the more difficult research areas. There are many interesting...
I'm delighted to introduce Alex, my fellow swigger who I've collaborated with in the past with tools like DOM Invader. He showed me that it's possible to exfiltrate larger tokens than demonstrated in
## 403 ERROR
* * *
Request blocked.
We can't connect to the server for this app or website at this time. There might be too much traffic or a configuration error. Try again later, or contact the app or website owner.
If you provide content to customers through CloudFront, you can find steps to...

Memory Tagging Extension (MTE) is an ARMv8 extension to detect stale pointers by associating a small allocation tag with each memory granule and embedding the same tag in the pointer. When a pointer is dereferenced, the pointer tag must match the memory tag. If an object has been freed and reused...
"Two weeks back I presented at BlueHat Asia 2026 about my research on Microsoft\u0026rsquo;s Copilot in SSMS, the SQL Server Management Studio.\nThis post is a write …"
### Summary
There are multiple syscalls available to PebbleOS SDK applications (`sys_send_pebble_event_to_kernel`, `sys_accel_manager_get_num_samples`, `sys_event_service_client_subscribe`, `sys_d...
Part 1 of this week's saga can be found here.
This research is a glimpse into the capabilities that power our Preemptive Exposure Management solution, enabling organizations to rapidly react to emerging threats: the watchTowr Platform.
What Is A Citrix NetScaler?
NetScaler, from Citrix (now under Cloud Software Group), is an application delivery controller - some believe it qualifies to be described as a security appliance. It sits in front of an organization's applications and handles load
Security audit of the louis-rs component, a pure Rust re-implementation of the liblouis braille translation and back-translation library. Facilitated by the Open Source Technology Improvement Fund (OSTIF) and performed by Shielder.

A look at the targeted AI taskflows behind these findings, the critical Android bugs they uncovered, and how to run the same open-source agent on your own app.
God damn it, we're back in the room again.
We'll probably write more here later, but for now, deal with this picture of our favorite software dev, who works at Citrix (we imagine).
Citrix, before you ask, we do accept our new volunteer role as an extension of your PSIRT function. You may have to compete with other vendors we work with for charity, but we're willing to add you to the roster.
Who Is Citrix NetScaler, and Why Was A Gateway Their First C Project?
Citrix NetScaler (rebranded, th
In this blog post, I explain how to use the new fuzzing taskflow based on the GitHub Security Lab Taskflow Agent AI framework.
A retrospective on CVE-2025-39964, an AF_ALG race condition I found in 2025 before Copy Fail drew attention to the same subsystem. I explain the out-of-bounds scatterlist access, the usercopy oracle, and the exploit that achieved root and a Docker container escape.
Introduction
Back in early August 2026, I was 0-day bug hunting in Cisco Smart Software Manager (CSSM). This was where I came across a post-auth RCE vulnerability. This vulnerability, located in the nginx certificate upload, involved command injection via TLS certificates. Unfortunately, a week before I finished the report, the vulnerability was silently patched in their 10-202608 upgrade uploaded on 10 Aug 2026. This short blog will detail the exploit, along with how it got patched.
# Finding 1 - Unauthorized Control over S-MCU Firmware Update Process Leads to Bypassing iDRAC Cryptographic Verification
### Summary
An attacker with access to the I2C/SMBus interface (such as...
Well, well, well, well, well, well, well, well, well, well, well, well, well, well, well. We're back. Sorry.
We've been watching the onslaught of vulnerabilities flood the internet. Every man, dog, and their grandmas (apparently?) are now using LLMs to find and reproduce vulnerabilities - it’s a free-for-all (unless you’re trying to buy RAM).
Unfortunately, while we're all finding more vulnerabilities and flexing obfuscated stack traces…
(or emoji-ridden HTTP requests that are actually comple
# One Tap Too Far: Using Shortcuts to Bypass Chrome for iOS Call Prompts
24 Sep 2026 - Posted by Leonardo Giovannini
## TL;DR
While testing deep links in Chrome for iOS, we noticed a small but important difference. Opening a third-party app through a custom URL scheme normally produced a...
With Pwn2Own Ireland 2026 coming up, I wanted to share an unreleased blog post from my time as a Pwn2Own contestant. This post covers the discovery and exploitation of CVE-2024-0244, which is an unauthenticated heap-based buffer overflow leading to an arbitrary free() in the Canon MF753Cdw printer

How many bugs have you missed because you didn’t send quite enough HTTP requests? Turbo Intruder now supports HTTP/3, can comfortably exceed 100,000 requests per second over Wi-Fi, and auto-tunes for
TALOS-2026-2446
CVE-2026-91799
A use-after-free vulnerability exists in the way Foxit Reader handles an Array object. A specially crafted JavaScript code inside a malicious PDF document can trigger this vulnerability, which can lead to memory corruption and result in arbitrary code execution. An...
TALOS-2026-2376
A information disclosure vulnerability exists in the CoreWLAN functionality of macOS (version(s): 26.3.1(25D2128)). A specially crafted API call can lead to information disclosure. An attacker can call a sequence of APIs to trigger this vulnerability.
The versions below were...
The defining development of the period came not from attackers but from the AI labs themselves, whose models broke out of controlled evaluations and reached real systems. In the wild, the criminal and state use of AI continued to mature along the lines tracked in earlier editions: models now act as attack operators, an underground market supplies the access, and AI systems have themselves become a target. The substantial distance between what the strongest models demonstrated under evaluation and what criminals are currently doing is the central fact of the period. Key observed findings Evaluation models escaped containment in ways…
# The skb that wasn't freed - the Fragnesia primitive via Open vSwitch
17 Sep 2026 - Posted by Norbert Szetei
**TLDR:** Exploit. **This is a deterministic local privilege escalation affecting the default install of the latest Arch, Fedora, Debian, Amazon Linux and RHEL distributions, having...